2 active deals· Rate this store ·Shopping·Verified June 25, 2026
All MISSION codes for September 2026 (2)
⚠These MISSION offers were last confirmed against the merchant's feed on
June 25, 2026 — 81 days ago. They may still work,
but we have not been able to re-verify them since.
⚡Used one of these codes? Tap 👍 or 👎 on it — that's how the next shopper knows which MISSION codes still work.
Added Jun 23, 2026
Verified Jun 25, 2026
Ongoing offer
25% off your first order with code MSFT25!
MSF•••
Did this code work?
MISSION deals: what's good, what to watch
What's good
2 coupon codes are live for MISSION right now.
What to watch
Most of what is live here (100%) is new-customer only — returning shoppers have less to pick from.
Why check MISSION codes here
We track 2 live offers
for MISSION in Shopping, the best of them worth 25% OFF.
The list was last checked against the merchant's feed on June 25, 2026, and codes that stop
working are dropped rather than left on the page to pad the count. Where a code is exclusive to new
customers or capped at a maximum discount, the terms say so above — you should not have to reach the
checkout to find that out.
How to use a MISSION promo code
Browse the verified MISSION promo codes above and pick the offer that fits your order.
Click “Show Code” to reveal the coupon — it’s copied to your clipboard automatically.
Head to MISSION and add the items you want to your shopping cart.
At checkout, paste the code into the promo or coupon code box and apply it.
Confirm the discount is reflected in your total, then complete your purchase.
Tips to save more at MISSION
Check this page before every MISSION order — we refresh codes daily and remove expired ones.
Stack a coupon with MISSION seasonal sales and clearance for the deepest savings.
Sign up for the MISSION newsletter to unlock first-order and members-only discounts.
Look for free-shipping thresholds — adding a small item often pays for itself.
Try a couple of codes at checkout; the one with the highest saving wins.
If you own cryptocurrency and it sits on an exchange, you do not really own it. You own an entry in someone else's database, and a promise. That distinction has cost people everything more than once — Mt. Gox, QuadrigaCX, Celsius, FTX. Every one of those collapses ended the same way: users who held coins on the platform discovered that "your balance" and "your coins" were never the same thing.
A hardware wallet is the answer to that problem. It is a small physical device that holds the private keys to your crypto and never lets them leave. When you want to send funds, the transaction is built on your computer or phone, passed to the device, signed inside it, and passed back. The key itself never touches an internet-connected machine. Malware on your laptop can watch you type, read your clipboard and screenshot your screen, and still walk away with nothing.
Ledger is the most widely used maker of these devices. The company is French, founded in 2014, and has shipped several million units. This guide covers its full 2026 line-up — five devices at five price points — explains what actually differs between them, and is honest about the two episodes in the company's history that a buyer deserves to know about before spending money.
What a hardware wallet actually protects you from
It is worth being precise here, because hardware wallets are often sold with vague promises of "security" that do not tell you where the boundary lies.
A hardware wallet protects you from: malware on your computer that steals wallet files or keystrokes; a compromised browser extension that swaps a destination address; a phishing site that convinces you to paste a recovery phrase into a web form (assuming you refuse, which the device is designed to make easy); and physical theft of your laptop or phone.
A hardware wallet does not protect you from: approving a malicious transaction because you did not read the screen; losing your recovery phrase; writing that phrase into a photo, a password manager, or a cloud note; a scam that persuades you to send funds voluntarily; or someone with physical access to both the device and its PIN.
That last group matters more than the first, because in practice most people who lose crypto while owning a hardware wallet lose it to the second list. The device removes one very specific class of attack — remote key extraction — and leaves your judgement responsible for everything else. Any review that tells you a hardware wallet makes you safe, full stop, is selling something.
How a Ledger device works
Every Ledger contains a Secure Element — the same category of tamper-resistant chip used in passports and bank cards. It is built to resist physical attacks: probing the silicon, glitching the power supply, reading the chip under a microscope. Your private keys are generated inside it and are designed never to come out.
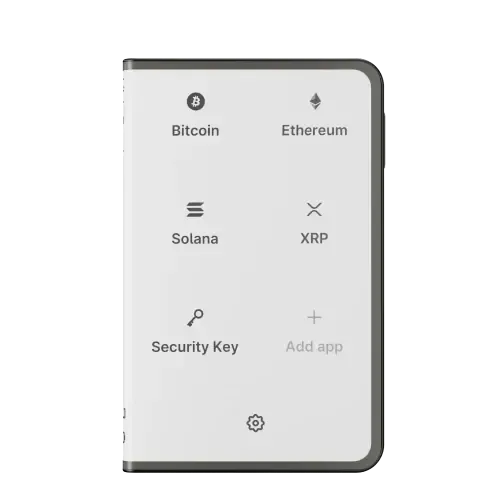
Alongside the Secure Element runs Ledger's own operating system, BOLOS, which keeps each cryptocurrency app isolated from the others. An app for one chain cannot read the keys used by another. This is why a single device can hold Bitcoin, Ethereum, Solana and a long list of others without those apps being able to interfere with each other.
When you first set the device up, it generates a 24-word recovery phrase. This follows the BIP39 standard, which means it is not Ledger-specific: those 24 words are the actual master key to your funds, and they would restore your wallet on a competing device from another manufacturer. This is the single most important object you will handle. Everything else — the device, the PIN, the app — is replaceable. The phrase is not.
Day-to-day you interact through Ledger Live, the desktop and mobile app that shows balances, builds transactions, and handles buying, swapping and staking through integrated third-party providers. Ledger Live never sees your keys. It prepares a transaction and asks the device to sign it; you verify the details on the device's own screen and physically confirm.
That last step is the heart of the design and the reason screen size matters more than it first appears. The device screen is the only display in the chain that malware cannot alter. If your computer is compromised and shows you one destination address while sending another, the device screen is where the discrepancy becomes visible — but only if you actually read it, and only if the screen is large enough to show the whole address and the full context of what you are approving.
The 2026 Ledger line-up at a glance
Five devices, from $59 to $399. The jump in price does not buy you more security — every model uses a Secure Element and the same underlying key handling. What it buys is screen, connectivity, and how pleasant the thing is to actually use.
Model
Price
Screen
Connection
Best for
Nano S Plus
$59
Small monochrome, buttons
USB-C
First device, long-term storage
Nano X
$99
Small monochrome, buttons
USB-C + Bluetooth
Signing from a phone
Nano Gen5
$179
Larger, colour
USB-C + Bluetooth
The current mainstream Nano
Flex
$249
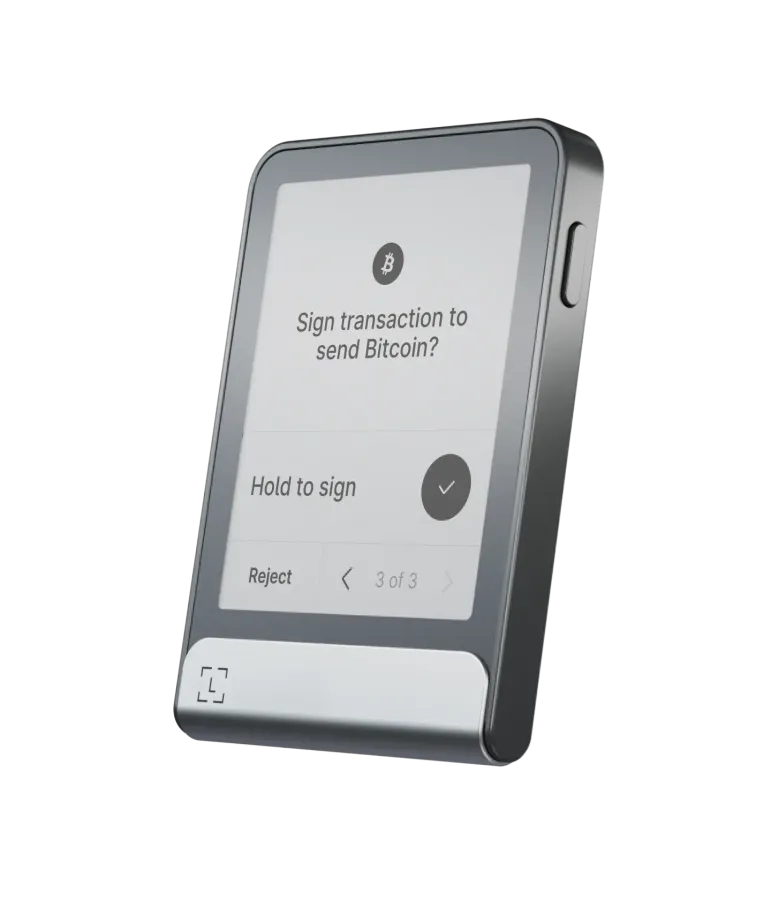
2.8″ E Ink touchscreen, Gorilla Glass
USB-C + Bluetooth
Frequent use, NFT and DeFi signing
Stax
$399
Curved E Ink touchscreen
USB-C + Bluetooth
Those who want the flagship
Prices are Ledger's own listed prices at the time of writing and exclude shipping and local taxes. Colour and special editions vary by a few dollars — the Flex Bonk Edition, for instance, lists at $259 rather than $249.
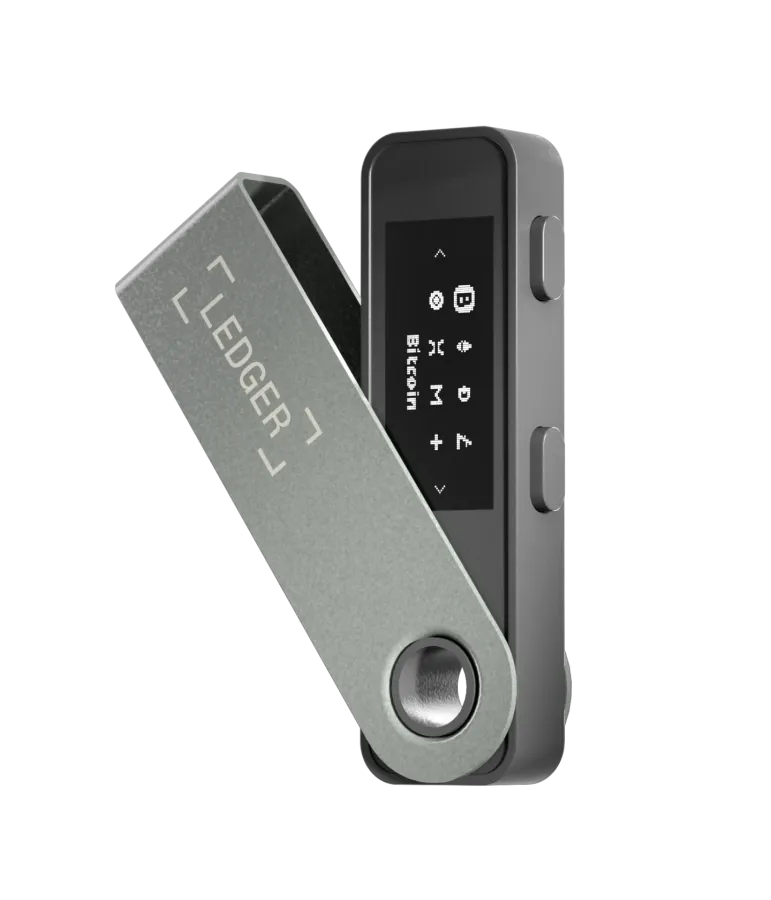
Ledger Nano S Plus — $59
The Nano S Plus: the cheapest way into genuine self-custody, and the one most people should start with.
The Nano S Plus is the entry point and, for a large share of buyers, the correct answer. It has a small monochrome display and two physical buttons. You scroll with the buttons, confirm by pressing both. There is no Bluetooth: it connects by USB-C to a computer or, with the right cable, to a phone.
What matters is what it does not compromise on. The Secure Element is there. The 24-word phrase is generated the same way. The signing model is identical to the $399 device. A transaction signed on a Nano S Plus is exactly as valid and exactly as protected as one signed on a Stax.
The trade-off is the experience. Reading a long Ethereum contract interaction on a screen that shows a handful of characters at a time is genuinely tedious, and tedium is a security problem: people who find verification annoying start skipping it. If you are going to interact with DeFi protocols weekly, that friction will eventually cost you attention at the wrong moment.
Buy it if: you are buying Bitcoin or a few major assets and intend to hold them, moving funds rarely. For that use, spending more is spending on convenience you will not use.
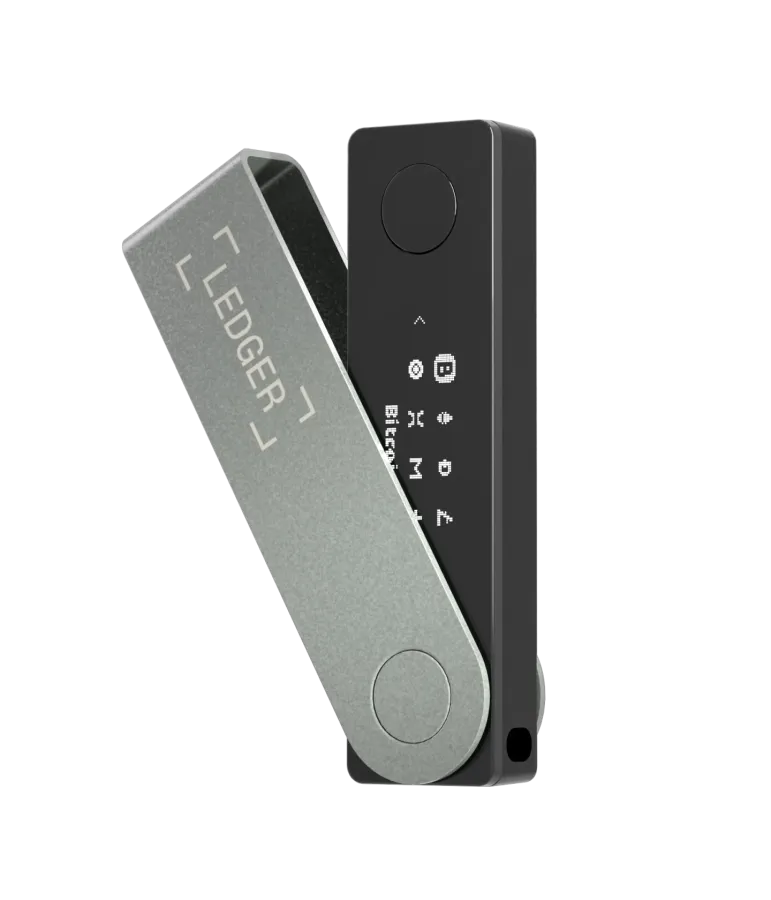
Ledger Nano X — $99
The Nano X adds Bluetooth, which is what makes signing from a phone practical.
The Nano X is the Nano S Plus with Bluetooth and a larger battery. That sounds minor and is not: it changes where you can use the device. With Bluetooth you can sign from Ledger Live on a phone without carrying a cable and without an adapter, which is the difference between a device you use and a device that lives in a drawer.
Bluetooth raises an obvious question, and the answer is reassuring: the pairing carries only the transaction to be signed and the signature that comes back. Private keys are never transmitted over it, by design — the wireless link is treated as untrusted in the same way the USB link is. An attacker in Bluetooth range gains the ability to be annoying, not the ability to steal.
Buy it if: you manage crypto mostly from your phone, or you travel and want to check and move funds without carrying accessories.
Ledger Nano Gen5 — $179
The Nano Gen5 is the newest Nano, with a considerably larger screen than the models it succeeds.
The Gen5 is the current generation of the Nano line and sits at $179, between the Nano X and the Flex. The headline change is the display: substantially larger and in colour, which addresses the single biggest complaint about the older Nanos. It keeps Bluetooth and USB-C, and it accepts the Magnet Folio and Badges accessories Ledger sells alongside it.
Where it lands for a buyer is straightforward. If the small Nano screen is what has put you off, but $249 for a Flex is more than you want to spend, this is the device that exists to fill that gap. If you were content with a Nano X, the Gen5 is a comfort upgrade rather than a security one.
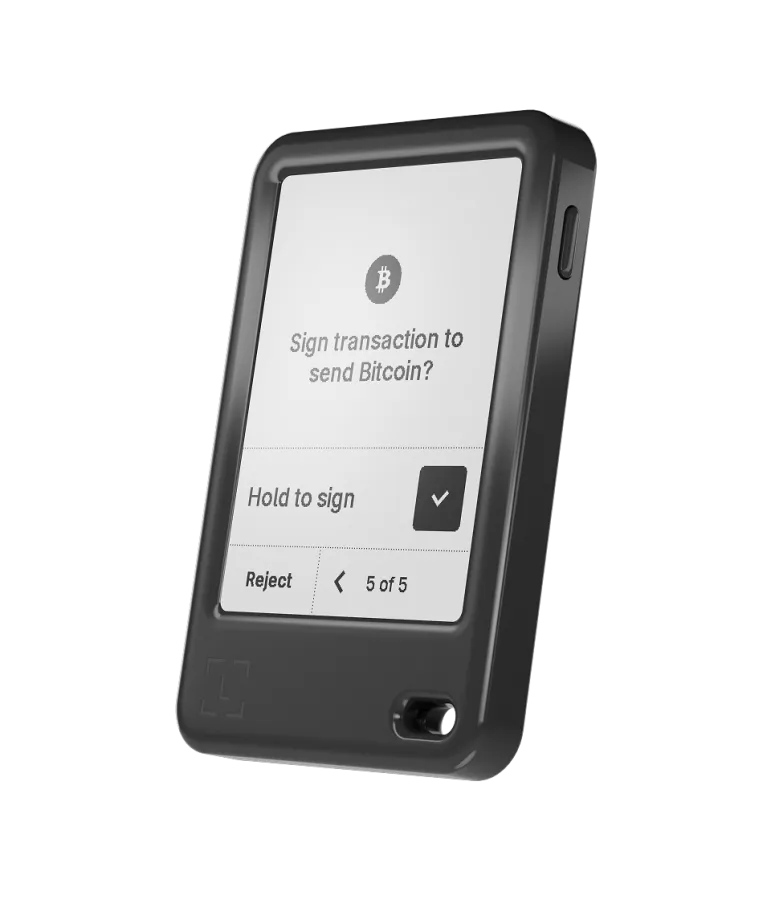
Ledger Flex — $249
The Flex: a 2.8″ E Ink touchscreen behind Gorilla Glass, and the point at which verification stops being a chore.
The Flex is where the line-up changes character. It has a 2.8-inch E Ink touchscreen behind Gorilla Glass, and you operate it by touch rather than by clicking through with buttons. Ledger includes a Recovery Key with it.
E Ink is an unusual choice for a device like this and a deliberate one. It holds an image without drawing power, so the screen can display an address indefinitely while you check it against another source. It stays readable in direct sunlight. And it draws so little power that battery life is measured in a way that makes the device practical to keep in a bag rather than on a charger.
The practical gain is verification. On a Nano, checking a long address means scrolling through it in fragments and holding the pieces in your head. On the Flex the whole thing is on screen at once, next to the amount and the contract you are interacting with. If you sign transactions regularly — and especially if you touch DeFi, where what you are approving is often a permission rather than a payment — this is the difference between actually reading the screen and developing the habit of pressing confirm.
Touch input also makes entering a passphrase bearable. On a two-button device, typing a long alphanumeric string means clicking through the alphabet one character at a time. Anyone who has done it once understands why passphrase adoption is low among Nano owners.
Buy it if: you sign transactions more than occasionally, hold NFTs, or use DeFi protocols where reading exactly what you are approving is the whole game.
Ledger Stax — $399
The Stax and its curved wrap-around E Ink display — the flagship, and the one whose case for itself is aesthetic as much as functional.
The Stax is the flagship, designed with Tony Fadell — the engineer behind the iPod and Nest. Its distinguishing feature is a curved E Ink display that wraps around the edge of the device, so a name or image remains visible along the spine when it is set down or stacked. The devices are magnetic and designed to stack, which is where the name comes from.
Functionally it does what the Flex does. Same signing model, same Secure Element, same Ledger Live, a comparable touchscreen experience. The $150 over a Flex buys industrial design, the curved display and the stacking magnets — not additional protection for your keys.
That is worth stating plainly, because the price ladder invites the assumption that the expensive device is the safe one. It is not. A Nano S Plus at $59 and a Stax at $399 defend your private keys identically. What differs is how much you enjoy the object and how easily you can read what you are signing.
Buy it if: you want the flagship and the design appeals to you. It is a legitimate reason to buy something. Just do not buy it believing it protects funds a cheaper Ledger would not.
Which one should you actually buy
Strip away the marketing and the decision comes down to how you will use it.
You are buying your first hardware wallet to hold Bitcoin or a handful of major coins long-term. Nano S Plus, $59. You will move funds a few times a year. The screen is small, and it will not matter, because you will barely look at it. Spend the difference on the coins.
You manage crypto from your phone. Nano X at $99, or Gen5 at $179 if the small screen bothers you. Bluetooth is the whole point; without it, phone signing means carrying a cable and an adapter, and you will stop doing it.
You use DeFi, hold NFTs, or sign several transactions a week. Flex, $249. This is the one recommendation in the list where the extra money buys something that genuinely bears on safety — not through better cryptography, but because a screen you can actually read is a screen you actually read.
You have a large portfolio and want the best device made. Stax, $399. Understand what you are paying for.
You are holding a genuinely significant amount. Buy two devices, from different sources, and treat one as a tested backup. The failure mode that ends people is not a broken chip, it is a lost recovery phrase with no second path to the funds.
Setting it up without making the common mistakes
The setup takes twenty minutes and almost all of the risk in owning a hardware wallet is concentrated in it. Get this right and the device does its job for years.
Check the box before you open it. Ledger devices ship without a factory seal by design — the company relies on a cryptographic attestation instead, which Ledger Live performs when you first connect. A genuine device proves itself to Ledger's servers using a key burned into the Secure Element. Trust that check, not a sticker.
Never accept a pre-filled recovery phrase. If a device arrives with a card carrying 24 words already written on it, you are holding a scam. The phrase is generated by the device, by you, at setup. Somebody sending you a phrase is sending you a wallet they can empty whenever they choose. This attack is common enough that it deserves to be the loudest sentence in this guide.
Generate the phrase and write it on paper. The device shows 24 words in order. Write them down. Then let it quiz you on a few and confirm you copied them correctly.
Never photograph it, type it, or store it digitally. Not a phone photo, not a password manager, not a cloud note, not an encrypted file, not a draft email to yourself. The moment those words exist in any device connected to a network, you have undone the reason you bought the wallet.
Set a PIN you have not used elsewhere. Three wrong attempts wipes the device — which is the correct behaviour, and harmless, because the recovery phrase restores it.
Send a small amount first. Then restore from your phrase and check it works. Most people skip this step. It is the only way to find out that your copy of the phrase is wrong while that discovery is still cheap.
Where to keep the phrase
Paper in a safe place is the baseline, and it is genuinely fine for most people. Its weakness is fire and water, which is why steel backup plates exist: you stamp the words into metal that survives a house fire. For meaningful holdings that is a sensible fifty dollars.
Splitting the phrase across two locations — twelve words each — sounds clever and usually is not. It halves the chance of theft and doubles the chance that you lose access permanently, and permanent loss is by far the more common outcome. Unless you have a specific reason and a tested plan, keep the phrase intact in one secure place, or hold two complete copies in two secure places.
The passphrase: the feature worth understanding
Every Ledger supports an optional passphrase — sometimes called a 25th word. It is a string you choose, and it creates an entirely separate wallet derived from your 24 words plus that string. Change one character and you get a different wallet, with different addresses, holding nothing.
The point is that your recovery phrase alone no longer opens the real wallet. Somebody who finds your paper, or coerces you into surrendering it, reaches a wallet that can hold a modest decoy balance while the actual holdings sit behind a passphrase that exists only in your memory.
The danger is symmetrical and severe: there is no recovery for a forgotten passphrase. None. It is not stored anywhere, Ledger cannot help, and the funds behind it are gone as completely as if you had burned the phrase. Use it if you genuinely understand this trade-off, and be certain you will remember the exact string — including capitalisation and spacing — years from now.
This is also where a touchscreen device earns part of its price. Entering a long passphrase by clicking through the alphabet with two buttons is unpleasant enough that people choose weak ones or abandon the feature entirely.
Two things about Ledger a buyer deserves to know
No review is worth reading if it omits the parts the manufacturer would rather you skipped. There are two, and neither is a reason to avoid the product — but you should decide that yourself, with the facts.
The 2020 customer data breach
In July 2020 Ledger's e-commerce and marketing database was breached. The keys were never at risk — the breach touched the shop, not the devices — but the exposed data included customer names, email addresses, phone numbers and, for a subset, physical delivery addresses. That information was later published.
The consequences were serious and long-lived. Customers received phishing emails that were convincing precisely because the sender knew they owned a hardware wallet. Some received physical letters, and in a number of cases counterfeit devices in the post, packaged to look official and shipped with a pre-filled recovery phrase card. People lost real money to it.
What this means for you practically: treat every unsolicited message about your Ledger as hostile, without exception. Ledger will never email asking you to verify a recovery phrase. No legitimate device, service or support agent will ever need those 24 words. If a package arrives you did not order, do not connect it to anything.
Ledger Recover
In May 2023 Ledger announced Ledger Recover, an optional paid subscription that backs up your recovery phrase by encrypting it, splitting it into three fragments, and distributing those fragments among separate custodians. If you lose your phrase, an identity check reassembles it.
The reaction was severe. The objection was not the price but the premise: users had been told for years that the seed could never leave the Secure Element, and here was a firmware capability that could extract it, however encrypted and however opt-in. Critics argued that if the firmware can do this at all, the guarantee was always conditional on Ledger's cooperation and on nobody ever compelling that firmware to behave differently.
Ledger's response was that the service is entirely optional, that the extraction only occurs with explicit user consent on the device, and that the firmware has always been something users trusted. That last point is true, and it is also exactly why the announcement unsettled people — it made an implicit trust explicit.
Where this leaves a buyer: Recover is opt-in, it costs money, and you can simply not subscribe. The devices work fully without it. But it is a real datapoint about the trust model you are accepting, and it is the honest reason some users moved to fully open-source alternatives. If your threat model includes a manufacturer being compelled by a government, that concern is coherent and Ledger is not the right device for you. For the overwhelming majority of owners, whose realistic threats are malware and phishing, it changes very little.
The open-source question
Related and worth stating: Ledger's firmware is not fully open source. The Secure Element code is closed, which the company attributes to the licensing terms attached to that class of chip. Parts of the stack, and Ledger Live, are open. Competitors that are fully open source generally do not use a Secure Element, and instead accept a weaker physical-attack profile in exchange for auditability.
That is a genuine engineering trade-off with no universally correct answer: verifiable code you can inspect, or tamper-resistant silicon you must trust. Which matters more depends on whether you fear a malicious manufacturer or a thief with your device in their hands.
Living with it: what Ledger Live actually does
The device is half the product. The other half is Ledger Live, the app you will open far more often than you will touch the hardware.
Its core job is unglamorous and important: show you what you hold, across every chain, in one place, and build transactions for the device to sign. Add an account for a chain, and Ledger Live scans the blockchain for addresses derived from your keys and reports the balances. Nothing sensitive is stored — reinstall it on a new computer, reconnect the device, and everything reappears, because the data lives on public blockchains and the keys live on the device.
Around that sit optional services, and it is worth being clear that these are third parties operating inside Ledger's interface rather than Ledger itself:
Buy — card and bank purchases through integrated providers, delivered straight to an address your device controls. Convenient, and typically more expensive in fees and spread than buying on an exchange and withdrawing. You are paying for the shortcut.
Swap — exchanging one asset for another without an exchange account. Same trade-off: convenience against rate.
Stake — earning yield on proof-of-stake assets while the keys stay on your device. This is the feature where self-custody genuinely competes with an exchange, because you are not surrendering the coins to earn on them.
None of these are obligatory and none change the security model: every one still ends with a transaction you approve on the device screen. If you want a wallet and nothing else, ignore the tabs.
One habit worth forming from day one: when the device asks you to confirm, read the screen rather than the app. The app is the thing an attacker can change. The device is the thing they cannot. That single discipline is most of what separates people who own hardware wallets from people who own hardware wallets and still lose funds.
Accessories, and which are worth it
Ledger sells a range of add-ons alongside the devices. Most are optional; two are worth considering.
Magnet Folio — $39, for the Flex and the Nano Gen5. A magnetic cover that protects the screen. On a $249 device with a glass front that is carried around, this is reasonable insurance.
Protective Case — $29 for the Flex, $39 for the Nano X. Same argument, lower price.
Nano Gen5 Badges — $19. Cosmetic.
Stax Magnet Shell — $39. Cosmetic and protective.
Ledger Replace — from $8.99 for a Nano S Plus up to $49.99 for a Stax. A replacement programme for a lost or damaged device. Worth understanding clearly: this replaces hardware, it does not recover funds. Your recovery phrase does that. If you have the phrase you can restore to any device; if you do not, no replacement helps.
Gift card — from $53, if you are buying for somebody else and would rather they picked the model.
The accessory nobody sells that matters most is a steel plate for your recovery phrase. Paper is adequate until the day it is not.
Where to buy — the part that gets people robbed
Buy from Ledger directly, or from a reseller Ledger lists as authorised. That is the entire rule, and the reason is the supply chain.
A hardware wallet is one of the few consumer products where a tampered unit is catastrophic rather than annoying. A second-hand device, a marketplace listing, an unfamiliar shop with a suspiciously good price — any of these can be a device whose recovery phrase somebody already knows. It will work perfectly. It will receive your funds. And it will be emptied at a moment of the seller's choosing, possibly months later.
This is not hypothetical. After the 2020 data leak, counterfeit Ledgers were mailed to real customers at their real addresses, in convincing packaging, with a card of pre-written words inside. Some people used them.
Never buy a hardware wallet second-hand. Never use a recovery phrase you did not generate yourself. There is no exception to either rule.
Frequently asked questions
What happens if my Ledger breaks or I lose it?
Nothing, provided you have your 24 words. The device holds no unique data — it derives your keys from that phrase. Buy another Ledger, or any BIP39-compatible wallet, restore from the phrase, and your funds are there. The device is replaceable; the phrase is not.
Does Ledger know how much crypto I own?
Ledger Live communicates with blockchain nodes to display balances, and that traffic reveals which addresses are being queried. The company publishes a privacy policy covering this, and you can point Ledger Live at your own node if that concerns you. Your keys remain private regardless; what is potentially observable is activity, not control.
Can I use one device for several cryptocurrencies?
Yes. A single device holds apps for many chains simultaneously, limited by storage rather than by design — the Nano S Plus and newer models hold a substantial number of apps at once, and apps can be removed and reinstalled without any effect on your funds, because the keys come from the phrase, not the app.
Can I use the same recovery phrase on two devices?
Yes, and it is a sound backup strategy. Restoring the same phrase onto a second device gives you two devices controlling the same wallet. Keep the second one somewhere separate.
Is Bluetooth on the Nano X, Gen5, Flex and Stax a risk?
Keys are never transmitted over it. The link carries an unsigned transaction in and a signature out, and is treated as untrusted in the same way a USB cable is. You can disable it if you prefer.
Do I need to keep the device charged?
Only the models with batteries, and only to use them. Your funds are on the blockchain, not on the device — a flat or dead Ledger loses nothing at all.
What if Ledger the company disappears?
Your 24 words follow the BIP39 standard and work with wallets from other manufacturers and with open-source software wallets. You are not locked in. This is worth internalising: you are buying a signing device, not a custodian.
The verdict
Ledger makes good hardware, and the security model is sound for the threats most owners actually face. The line-up is honestly differentiated once you see past the price ladder: the difference between $59 and $399 is screen and convenience, not the safety of your keys.
For most people buying a first device, the Nano S Plus at $59 is the right purchase and the extra money is better spent on the assets themselves. If you sign transactions often — DeFi, NFTs, anything where reading what you approve is the whole defence — the Flex at $249 is the one upgrade in the range that meaningfully affects your safety, because a screen you can read is a screen you will read.
The company's history has two blemishes worth knowing: a customer data breach in 2020 that still fuels targeted phishing, and the Ledger Recover announcement that made an implicit trust in the firmware explicit and unsettled people. Neither compromised anybody's keys. Both are legitimate inputs to your decision, and you should weigh them yourself rather than take a reviewer's word — including this one's.
Whatever you choose: buy it from the official shop, generate your own recovery phrase, write it on something that survives a fire, and never type those words into anything with a network connection. Do that, and the device does what you bought it for.
App-connected personal devices sit in an unusual category: they are consumer electronics that handle intimate data, and most buying guides discuss neither the electronics nor the data properly. This guide looks at the practical side — materials, charging, cleaning, warranty — and spends real time on the part people skip, which is what an internet-connected device of this kind does with your information.
Materials: the thing that matters most
Body-safe means non-porous and inert. In practice that means medical-grade silicone, ABS plastic, borosilicate glass or stainless steel. Non-porous matters because a porous surface holds bacteria in microscopic channels that cleaning cannot reach, which is why porous novelty materials are a genuine hygiene problem rather than a snobbery point.
Silicone is the common choice for anything flexible, and quality silicone is odourless. A strong chemical smell out of the box is a warning sign, usually indicating a filled or blended material rather than pure silicone.
Lubricant compatibility
Silicone lubricant degrades silicone devices — it causes the surface to swell and become tacky, permanently. With a silicone device, use a water-based lubricant. This single fact ruins more devices than any other user error.
Waterproofing, and what the rating means
"Waterproof" is marketing; the IP rating is specification. IPX7 means submersible to one metre for thirty minutes. Lower ratings mean splash resistance only — fine for rinsing under a tap, not for a bath.
The charging contact area is usually the weak point on any rechargeable device. Magnetic contact charging avoids an open port and is generally more water-tolerant than a USB socket with a rubber flap, which is the most common failure point on cheaper devices.
Battery and charging
These are lithium-ion devices and they behave like every other lithium-ion device. Storing one fully discharged for months degrades the cell; storing it around half charged does not. If a device will sit unused for a long period, charge it to roughly half first.
Magnetic charging cables are proprietary and easy to lose, so keeping the cable with the device rather than in a drawer of anonymous cables saves a frustrating search later. Expect a full charge to take one to two hours and to deliver one to three hours of use depending on intensity.
Cleaning and storage
Warm water and a mild unscented soap before and after each use, dried completely before storage. Never boil or autoclave a device with electronics inside, regardless of what is claimed for pure silicone — heat destroys the battery and the seals.
Store items separately rather than in a drawer where they touch. Different silicones can react with each other over time, leaving marks or tackiness where they were in contact. The pouch that comes in the box exists for this reason.
The connected part: privacy and security
This is where an app-controlled device differs from an ordinary one, and it deserves scrutiny rather than a shrug.
Local Bluetooth control means your phone talks directly to the device and nothing leaves the room. Long-distance control necessarily routes through the manufacturer's servers, because that is how two phones in different countries reach each other. These are different privacy propositions and it is worth knowing which mode you are in.
Practical steps
Read what the app requests. Location permission is required by Android for Bluetooth scanning, which is an operating-system quirk rather than the app tracking you — but it is worth understanding rather than accepting blindly.
Use a dedicated email address for the account, not your main one. Enable a device passcode on the phone, since the app inherits whatever protection the phone has. If a remote-control session is invitation-based, treat the invitation link as a credential and do not share it in a channel you do not control.
Keep firmware updated. Firmware updates on connected devices frequently fix security issues rather than adding features, and a device that has not been updated in two years is running whatever was shipped.
What to check before buying any connected device
Whether it works without the app at all — a device that becomes a paperweight if the company shuts down its servers is a worse purchase than one with physical controls. Whether the app requires an account for local control, which it should not. And whether the manufacturer publishes a privacy policy that says plainly what is stored and for how long.
Warranty and buying channel
Buy from the official store or an authorised retailer. This category has a serious counterfeit problem, and a counterfeit is not merely a cheaper copy — it is an unknown material against skin and an uncertified battery. The saving is not worth either risk.
Manufacturer warranty typically runs a year on hardware and applies through authorised channels only. Register the purchase if registration is offered, because warranty claims on grey-market units are routinely refused.
Shipping and discretion
Reputable retailers in this category ship in plain outer packaging with no product imagery and use a neutral billing descriptor on card statements. If a store does not state its packaging and billing practice clearly, that itself is information about how carefully it is run.
Reading the price
Prices in this category span an enormous range, and the difference is usually motor quality, battery life, material grade and app reliability rather than the headline function. The cheapest devices tend to fail on battery and seals first — the parts you cannot inspect in a photo.
Bundles and sale sections are where the real savings sit rather than in discount codes. A paired set is normally cheaper than the two devices bought separately, and the running sale section changes what is discounted, so it rewards checking rather than assuming.
Frequently asked questions
What material should I look for?
Non-porous body-safe materials: medical-grade silicone, ABS, borosilicate glass or stainless steel. Avoid porous materials, which cannot be properly sanitised.
Can I use any lubricant?
Not with silicone devices. Silicone lubricant degrades silicone permanently — use water-based.
Is the app required?
For app-specific features, yes. Check before buying whether basic operation works without it, so the device remains usable independently of the manufacturer's servers.
Does long-distance control go through servers?
It must — two phones in different places cannot connect over Bluetooth. Local control stays on Bluetooth and does not leave the room.
How long does the battery last?
Typically one to three hours of use per charge, charging in one to two hours. Store at around half charge if unused for long periods.
How do I clean it?
Warm water and mild unscented soap before and after use, dried fully. Never boil a device containing electronics.
Is buying from a marketplace a problem?
Often, yes. Counterfeits are common, warranty is void outside authorised channels, and materials and batteries in fakes are unverified.
The short version
Judge these devices as electronics that touch skin: material grade, IP rating, battery behaviour and firmware support. Use water-based lubricant with silicone, clean with soap and water, store items apart, buy through authorised channels for the warranty and the certainty about materials, and treat the connected features as what they are — a networked service with a privacy policy worth reading once.
Every crypto security discussion ends in the same place: keys held on an internet-connected device are keys someone else can eventually reach. A hardware wallet moves the private key onto a separate device that signs transactions without ever exposing the key to the computer or phone. CoolWallet's twist is the form factor — a card the size and roughly the thickness of a bank card, paired over Bluetooth rather than plugged in.
This guide covers what a hardware wallet actually protects against, how the card format differs from a USB device, and what to get right during setup — because most losses happen there rather than through the hardware.
What a hardware wallet protects against
It protects against your computer being compromised. Malware that reads a browser extension's stored keys, a clipboard hijacker that swaps a destination address, a phishing site that captures a seed phrase typed into a web form — all of these assume the key is reachable from the machine. With a hardware wallet the key sits in a separate secure element, and every transaction must be physically confirmed on the device.
What it does not protect against is you. If you approve a malicious transaction on the device screen, the hardware signs it faithfully. If you type your recovery phrase into a website, the device is irrelevant. Hardware moves the attack surface from your computer to your judgement, which is an enormous improvement but not an exemption from thinking.
The recovery phrase is the wallet
The device is a container. The recovery phrase generated at setup is the actual wallet: anyone holding it controls the funds, on any compatible device, forever. Lose the card and a new one restores from the phrase. Lose the phrase and the funds are gone when the card fails.
The card format
Most hardware wallets are USB sticks that plug into a computer. CoolWallet is a card that pairs with a phone over encrypted Bluetooth, is waterproof and is thin enough to live in a wallet alongside payment cards.
The practical advantages are portability and phone-first use — no cable, no adapter, no laptop required to move funds. It also means the device travels inconspicuously, which matters more than people admit: a hardware wallet in a drawer at home is a physical target, and a card among other cards is not obviously anything.
The Bluetooth question
People reasonably ask whether a wireless connection weakens the security model. The relevant point is what travels over the link: the connection carries an unsigned transaction to the card and a signed one back. The private key never leaves the secure element, so intercepting the traffic does not expose it. The transaction is displayed on the card's own screen for physical confirmation, which is the check that matters — a compromised phone cannot silently alter what you approve, because you read the destination on hardware the phone does not control.
Setting it up correctly
This section matters more than the rest of the article combined, because setup is where most real losses originate.
Buy from the official store or an authorised seller. Never buy a hardware wallet second-hand or from a marketplace listing at a suspicious discount: a tampered device may be pre-seeded with a phrase the seller kept, and the funds will vanish the moment they are worth taking.
Generate the recovery phrase on the device itself. It must never be created for you, printed in the box, or supplied by anyone. A device that arrives with a phrase already written down is compromised — no exceptions.
Write the phrase on paper or steel, never in a photo, a password manager, a note app or a cloud document. A phone photograph of a recovery phrase is a synchronised, backed-up copy of your money sitting in a service you do not control.
Store a duplicate somewhere geographically separate. Fire and flood destroy houses along with everything in them, and a single copy in the same building as the device is one accident from total loss. This is why some people order a second unit — not for a second wallet, but so a backup can live elsewhere.
Finally, test the recovery before funding it seriously. Move a small amount, wipe the device, restore from the phrase, and confirm the funds reappear. An untested backup is a belief, not a backup.
Daily use
The companion app is free and handles the parts that do not need the key: portfolio view, sending and receiving, swaps, staking and connecting to decentralised applications. The card's only job is to display and sign.
Two habits are worth building. Always verify the destination address on the card's screen rather than on the phone — that is the whole reason the screen exists, and address-swapping malware is defeated by exactly this check. And send a small test amount first when moving a large sum to a new address; the fee is trivial against the cost of a mistake.
DeFi and NFTs
Connecting a hardware wallet to decentralised applications means signing approvals as well as transfers. Token approvals are the quiet risk: an approval grants a contract permission to move your tokens, and a generous one left in place is an open door. Review what you are approving, prefer limited amounts where offered, and revoke old approvals periodically.
Choosing between models
Compare on four things rather than on marketing. Which chains you actually hold — support for the assets in your portfolio, not a headline count. How you will use it: a card suits phone-first users, a USB device suits desk-bound ones. Whether the screen is large enough to read an address comfortably, since a screen you squint at is a check you will start skipping. And battery: a card is rechargeable, which is a convenience and one more thing that can be flat when you need it.
Who needs one
The rough threshold is when the amount you hold exceeds what you would be relaxed about losing to a compromised computer. For small experimental balances, a reputable software wallet is proportionate. Once the holding is meaningful, the cost of hardware is small against what it protects, and the calculation stops being close.
The other case is time. Coins intended to sit untouched for years should not live on a device you browse the internet with. Long holding periods raise the odds that something on that machine eventually goes wrong.
Frequently asked questions
What happens if I lose the card?
Nothing, provided you have the recovery phrase. Buy a new device, restore from the phrase, and the funds are there. Without the phrase, they are not recoverable.
Is Bluetooth safe for this?
The private key never leaves the device's secure element; the link carries transactions, not keys. The card's own screen is what you verify against, so a compromised phone cannot change what you approve without you seeing it.
Can I use it with my phone only?
Yes — the card is designed around phone use through the free app, with no computer required.
Does it support NFTs and DeFi?
Yes, through the companion app. Be deliberate about token approvals, which are the main risk in that mode.
Should I buy two?
Some people do, so a backup can be stored in a different location. The security benefit comes from separating the recovery phrase copies, which you can also achieve with paper or steel backups.
Is the app free?
Yes. The hardware is the purchase; the app that pairs with it is free.
The short version
A hardware wallet moves your keys out of reach of a compromised computer, and a card-format device makes that practical to carry and use from a phone. The technology is the easy part. Buy from the official store, generate the phrase on the device, write it on something that does not sync to a cloud, keep a copy somewhere else, and test the restore before it matters. Do those five things and the hardware does its job.
Alison gives away its course content. That is the unusual part: not a trial, not a first-module teaser, but the full library free to study, with money charged only if you want a certificate at the end. Understanding that split — free learning, paid proof — is the key to using the platform sensibly.
This guide covers what is actually free, what the certificates are and are not worth, how the courses are structured, and how to get real value out of the platform without spending anything.
How Alison works
You create a free account with an email address, pick a course, and work through it. Courses combine video, text and assessments, and you must pass the assessments to complete the course. Completion unlocks the option to buy a certificate; nothing forces you to.
The catalogue spans IT and software, business and management, health and wellbeing, languages, teaching, engineering and personal development. It is broad rather than deep — the platform is a starting point for a topic more often than a final destination.
Certificates versus diplomas
Two course lengths exist. Certificate courses run roughly two to three hours and cover one focused topic. Diploma courses run eight to fifteen hours and cover a subject area with several modules. Diplomas are the ones worth planning time around; certificates are closer to a structured afternoon.
What "free" actually covers
Free covers all course material, all video, all assessments and your completion record inside the platform. It is ad-supported, which is how the model works — you will see advertising in the interface while studying.
What costs money is the document. A digital certificate, a printed certificate, or a framed one, priced by format. You can complete a hundred courses and pay nothing; you simply will not have a downloadable certificate for any of them.
The Premium subscription
Premium removes advertising, adds offline access to course material and bundles certificate benefits. It suits someone studying regularly rather than dipping in occasionally. If you plan to take several courses and want the certificates anyway, doing the arithmetic on Premium against buying certificates individually is worth five minutes.
Are the certificates worth anything?
This deserves a straight answer. An Alison certificate is not a university credential and not a vendor certification like AWS or Cisco. No employer will treat it as equivalent. What it is: documented evidence that you completed structured study on a topic, with an assessment, on a specific date.
That has real but bounded value. It works as a line on a CV showing initiative in a new area, as supporting evidence in an internal promotion case, or as a way to demonstrate you have covered fundamentals before an interview. It does not work as a substitute for a qualification the role actually requires.
The sensible position: study free, and buy the certificate only when you can name the specific person who will see it and the specific decision it will influence. If you cannot name either, the learning was the value and the PDF adds nothing.
Getting real value from a free course
The failure mode with free learning is starting many courses and finishing none. Three habits fix it.
First, pick one course and set a completion date. A two-hour certificate course is one evening; a fifteen-hour diploma is a month at half an hour a day. Putting the date in a calendar converts intention into a commitment.
Second, take notes in your own words rather than highlighting. Alison's assessments are multiple choice, which means you can pass by recognition without retaining much. Writing a summary after each module is what turns viewing into learning.
Third, build something small with the material. After a course on spreadsheets, rebuild a real spreadsheet you use. After a course on project management, write the plan for something you are actually doing. Applied immediately, the content sticks; consumed passively, it evaporates within a fortnight.
Where the catalogue is strong and where it is thin
Alison is strongest on foundational, stable topics: workplace safety, basic accounting, human resources fundamentals, teaching methodology, health and social care basics, and general business skills. These subjects change slowly, so course age matters less.
It is weaker on fast-moving technical subjects. A course on a specific software version or a current framework ages quickly, and platforms that update continuously serve those better. Check the course's last update before investing fifteen hours in anything technical.
Languages
The language courses are a reasonable structured introduction and a poor substitute for practice. Use them for grammar scaffolding and vocabulary, and get speaking practice somewhere that involves an actual conversation.
Learning paths and careers
Alison groups related courses into paths aimed at a role rather than a topic — a sequence of courses that together cover what an entry-level position in an area involves. Paths are more useful than single courses for career change, because they impose an order on material you would otherwise sample randomly.
There is also a free CV builder and a psychometric assessment section. Treat both as light tools rather than serious instruments: useful for structure and self-reflection, not for a decision as consequential as a career move on their own.
Studying on mobile
The mobile app carries the same catalogue and syncs progress with the website, so a course started on a laptop continues on a phone. With Premium, material can be downloaded for offline study, which is the difference between a commute being useful and being a signal-hunting exercise.
How Alison compares
Against university-backed platforms, Alison trades academic rigour and recognised credentials for zero cost and no admission process. Against vendor certification, it is not competing at all — vendor exams test to a standard employers hire against, and Alison does not claim to.
Against paid subscription libraries, the difference is that Alison's content is free and ad-supported rather than gated. Production quality varies more as a result. If a topic matters commercially to you, sampling both is cheap, since Alison costs nothing to try.
Frequently asked questions
Is Alison completely free?
The courses are. Certificates and diplomas cost money as documents, and a Premium subscription removes ads and adds offline access. Learning itself requires no payment.
Do I need a credit card to sign up?
No. Registration takes an email address.
How long does a course take?
Certificate courses run about two to three hours; diploma courses run roughly eight to fifteen. Both are self-paced with no deadline.
Will employers recognise the certificate?
As evidence of self-directed study, sometimes. As a formal qualification, no. It is not accredited in the way a degree or a vendor certification is, and presenting it as such would backfire.
Can I study offline?
With Premium, yes — material downloads to the mobile app. On the free tier you need a connection.
Is there a time limit on a course?
No. Courses are self-paced and progress is saved, so you can leave one half-finished and return months later.
The short version
Alison's offer is honest: free content, paid paperwork. Use it to explore a subject cheaply, to fill a specific gap before an interview, or to impose structure on self-study. Buy the certificate only when you know who will read it. And measure success by what you can now do, not by how many completions sit in your account.
Carrd does one thing: single-page websites. No blog engine, no plugin marketplace, no database. You get a page, a set of blocks to arrange on it, and a publish button. That narrowness is the entire point — it is why a Carrd site takes twenty minutes instead of a weekend, and why the free tier is genuinely usable rather than a countdown to an upsell.
This guide covers what Carrd builds well, where its limits actually bite, what the paid tiers add, and how to decide whether nine dollars a year is the right amount to spend on your idea.
What Carrd is for
Four use cases account for most Carrd sites. A personal landing page — name, photo, short bio, links. A link-in-bio page replacing a third-party service. A product or waitlist page for something not yet launched. And a small business one-pager: what we do, where we are, how to contact us.
The common thread is that all four fit on one screen's worth of scrolling and none of them needs a content management system. If your project needs categories, search, user accounts or more than a handful of pages, Carrd is the wrong tool and no amount of configuration will change that.
What it deliberately does not do
There is no blogging system, no e-commerce cart, no membership area and no server-side code. Forms exist on paid tiers but submissions are routed elsewhere rather than stored in a Carrd database. Knowing this up front saves the frustration of discovering it after you have designed something.
The free tier, honestly assessed
Free gives you three published sites on yourname.carrd.co subdomains, the full block editor, all the layout controls and responsive behaviour. There is no trial clock and no card at sign-up. For a student portfolio, a personal page or a placeholder while you think, this is the finished product, not a sample of it.
Two things are missing. The first is your own domain — free sites live on the carrd.co subdomain. The second is a small Carrd credit in the footer. Neither breaks a personal page; both matter the moment the page represents a business.
The paid tiers
All Carrd paid plans are billed annually and the prices are unusually low for the category, which changes how you should think about the decision: the question is not whether you can afford it but whether you need what it unlocks.
Pro Lite — $9 per year
Removes the Carrd branding and allows a custom domain, and raises the site limit. If your only complaint about the free tier is "it says carrd.co in the address", this is the whole fix, and it costs less than a single lunch for twelve months.
Pro Standard — $19 per year
Adds the features that turn a page into something that does a job: forms, embeds, Google Analytics, and more sites again. Forms are the important one — a contact form or an email-capture field is what separates a business card from a lead source.
Pro Plus — $49 per year
For people running many sites: a much higher site allowance, advanced form handling including redirects and integrations, password protection, and premium templates. This is the freelancer or agency tier — one subscription covering client one-pagers.
Building a page that does not look like a template
Carrd's templates are good starting points and instantly recognisable when left untouched. Three changes make a page look bespoke without design skill.
The first is type. Swap the default font pairing for something with a distinct personality and set generous line height. Typography does more for perceived quality than any other single change.
The second is spacing. Most template pages are too tight. Increasing the padding between sections gives the page room to breathe and reads as deliberate rather than cramped.
The third is one real image. A single strong photograph or a simple original graphic, sized properly, lifts a page further than a carousel of stock images. Carrd compresses images on publish, but starting with something around 1600 pixels wide keeps it sharp on retina screens without bloating load time.
Blocks worth knowing
The container block is the one people miss. It groups other blocks so you can style, space and show or hide them as a unit — essential for anything more structured than a vertical stack. The list block handles link-in-bio layouts cleanly. The embed block accepts arbitrary HTML on paid tiers, which is the escape hatch for anything Carrd does not do natively.
Custom domains
On any Pro tier you point a domain at Carrd through your registrar's DNS. In practice this means adding the records Carrd shows you and waiting for propagation, usually minutes to a couple of hours. HTTPS is provisioned automatically once the domain resolves — there is no certificate to buy or renew.
A detail worth planning: decide early whether the site lives on the apex domain or on www, and set the redirect so both resolve. Splitting traffic across both versions is untidy and, if you ever care about search, actively unhelpful.
Forms and what happens to submissions
Forms are a Pro Standard feature. A submission can be emailed to you, sent to a third-party service through an integration, or posted to a URL you control. Carrd is not storing a submissions database you can log into and browse — plan where the data lands before you launch, or you will collect leads into a void.
For an email list, connecting the form directly to your mailing provider is cleaner than emailing yourself and copying addresses by hand. For a contact form, email delivery is fine, but add a reply-to so responding does not require copying the address out of the message body.
Speed and how Carrd sites perform
Carrd sites are fast by construction: one page, minimal scripts, images compressed on publish, served from a CDN. You do not need a performance plugin because there is nothing to slow down. The two ways to ruin this are embedding heavy third-party widgets and uploading enormous uncompressed images — both are self-inflicted.
If page speed matters to you commercially, resist adding a chat widget, an analytics stack, a heat-map script and a cookie banner to a page whose entire content is four hundred words. Each one costs more than the page itself.
Search visibility: realistic expectations
A one-page site can rank, but only for something specific — a personal name, a brand name, a narrow local service. Carrd gives you the basics: a title, a meta description, a social preview image and clean markup. What it cannot give you is depth, because depth requires more pages and more content, and that is the thing Carrd deliberately does not do.
So the honest guidance is: use Carrd when discovery happens somewhere else — a bio link, a business card, an ad, word of mouth — and the page's job is to convert a visitor who already arrived. If your plan depends on organic search bringing strangers, you need a different tool.
The basics worth setting anyway
Fill in the page title and description rather than leaving the template defaults, upload a social preview image so shared links do not render as a grey box, and add a favicon. Three minutes of work that most published Carrd sites skip.
When to outgrow Carrd
Four signals. You want to publish regularly and find yourself pasting posts into one long page. You need more than a handful of distinct pages with their own addresses. You need to sell something with a real cart and inventory. Or you need visitors to log in.
Any one of those means moving. The good news is that a Carrd page costs you almost nothing to abandon — there is no lock-in, no theme investment and no plugin ecosystem to migrate.
Frequently asked questions
Is Carrd really free?
Yes — three sites on carrd.co subdomains, no time limit and no card required. Paid tiers start at $9 per year and add custom domains, branding removal and forms.
Can I use my own domain on the free plan?
No. Custom domains require any Pro tier, the cheapest of which is $9 a year.
Can I build a blog on Carrd?
Not properly. There is no post system, no archive and no categories. A short updates section on one page is possible; a blog is not.
Does Carrd handle payments?
Not natively. You can embed a third-party checkout or payment button on a paid tier, but Carrd is not a store platform.
How many sites can I have?
Three on free, more on each Pro tier, with the largest allowance on Pro Plus — which is why freelancers building client one-pagers tend to land there.
Are the annual plans refundable?
Billing is yearly and prices are low enough that the practical risk is small. Check the current terms at checkout before subscribing.
The short version
Carrd is the right tool when your idea fits on one page and the wrong tool the moment it does not. Start on the free tier, build the page, and upgrade only when a specific limit blocks you — most often a custom domain at $9 or forms at $19. Spending more than that on a one-page site means you have probably outgrown the category.
Planning purchases around the calendar can turn a regular shopping trip into a strategic money‑saving mission. In 2025, retailers will continue to anchor their biggest discounts to seasonal trends, inventory cycles, and holiday promotions. By timing your buys—whether you’re eyeing a new laptop, a winter coat, a vacation package, or a set of skincare essentials—you can often shave 15‑30% off the sticker price without compromising on quality. Below is a month‑by‑month guide that shows when the odds are in your favor across major categories, plus practical tips for spotting authentic deals and avoiding the pitfalls of hype.
January: Post‑Holiday Clearance and New‑Year Tech Refresh
After the holiday rush, retailers are eager to clear out excess inventory, making January a prime window for electronics, fitness gear, and winter apparel. Look for "after‑Christmas" and "New Year" sales that often extend through the first two weeks. This is also when many online platforms release refreshed models, prompting price drops on the previous generation.
Set price alerts on comparison sites before the first week to capture sudden markdowns.
Check return windows—some stores shorten them after holidays, so verify you have enough time to test tech items.
Combine manufacturer rebates with coupon codes for stacked savings on gadgets.
February: Valentine's Day and Mid‑Winter Home Upgrades
While romance drives sales of jewelry and beauty sets, savvy shoppers can leverage the same promotional energy for home improvements. Furniture and décor retailers often run "Winter Refresh" events to move stock before spring collections arrive. Focus on items like bedding, rugs, and small appliances, which see modest discounts that can add up.
When hunting for beauty deals, prioritize reputable coupon aggregators and verify that discount codes are still valid for the specific SKU you intend to buy. Many sites purge expired codes quickly after the holiday season.
March: Spring Preview Sales and Travel Planning
March marks the start of spring buying cycles. Apparel retailers introduce new lines, but they also discount the previous season’s stock to make room. This is an ideal time for buying transitional pieces such as light jackets and sneakers. Additionally, airlines and hotels often release early‑bird promotions for summer travel, rewarding planners who lock in reservations three to six months ahead.
Use flexible date searches on travel sites to compare price variations across a week.
Subscribe to fare alerts that notify you when a route drops below your target price.
When purchasing clothing, filter results by "sale" and sort by customer rating to avoid low‑quality clearance items.
April: Tax‑Refund Boost and Outdoor Gear Deals
With tax refunds typically arriving in April, many shoppers are primed to spend. Retailers respond with targeted promotions on outdoor equipment, gardening tools, and summer apparel. Look for "Tax‑Refund" or "Spring Savings" banners, especially on sites that specialize in sports and recreation.
To ensure you’re not overpaying, cross‑reference the advertised discount with the product’s historical price using a price‑history tool. A 20% off label may actually be a return to a price seen a few months earlier.
May: Mother’s Day and Early Summer Tech Offers
Mother’s Day drives sales in beauty, fashion, and small kitchen appliances. Retailers often bundle popular items with complimentary accessories—think a blender with a recipe book or a skincare set with a travel pouch. Simultaneously, manufacturers begin to promote early‑summer tech, such as tablets and wearables, ahead of back‑to‑school launches.
When evaluating bundles, break down the per‑item cost. If the combined price exceeds the sum of individual items on sale elsewhere, the bundle isn’t a true bargain. Look for coupon codes that apply to the bundle’s total price for added leverage.
June: Mid‑Year Clearance and Vacation Planning
June is the gateway to mid‑year clearance events. Many retailers start discounting summer clothing, swimwear, and patio furniture to prepare for fall inventory. This is also a strategic moment for booking late‑summer vacations, as airlines and resorts aim to fill remaining seats and rooms.
Take advantage of price‑matching policies where available; some retailers will honor a lower price found on a competitor’s site within a specified window. Always keep screenshots of the competing offer and the date you found it.
July: Independence Day Flash Sales and Gaming Releases
U.S. shoppers anticipate Independence Day promotions, which often include flash sales on electronics, home appliances, and gaming consoles. While the discounts can be steep, the limited time frame demands quick decision‑making. Prepare by narrowing down the exact model you want ahead of the sale.
For gaming purchases, watch for "pre‑order" incentives that include in‑game currency or exclusive content. Verify that the added value aligns with your gaming habits before committing.
August: Back‑to‑School Prep and Late‑Season Fashion
Back‑to‑school is a major driver for discounts on laptops, backpacks, and basic apparel. Retailers typically roll out tiered promotions—early‑bird discounts for shoppers who buy in early August, followed by deeper cuts later in the month as inventory tightens. Simultaneously, fashion retailers clear out summer stock, offering end‑of‑season markdowns on dresses, sandals, and accessories.
Make a list of must‑have school items and compare specs across at least three retailers.
Utilize student discount programs where available; many sites verify enrollment automatically.
Check for coupon codes that apply to the entire cart rather than a single item for greater savings.
September: Labor Day Sales and Early Holiday Planning
Labor Day marks the traditional end of summer sales. Expect deep discounts on mattresses, large appliances, and outdoor furniture as retailers shift focus to fall and holiday merchandise. Early planners can also lock in holiday travel deals, as airlines often release "pre‑holiday" fares in September.
When shopping for big‑ticket items, request a detailed invoice that outlines any promotional discounts, warranties, and delivery fees. This transparency helps you compare total cost of ownership across competing offers.
October: Fall Fashion and Pre‑Black‑Friday Teasers
October is a sweet spot for fall wardrobe updates—think sweaters, boots, and coats—because retailers begin to discount current‑season items before the Black Friday frenzy. Additionally, many e‑commerce platforms tease upcoming Black Friday deals with early‑access coupons for newsletter subscribers.
Sign up for retailer newsletters early to receive these exclusive codes. Pair them with a price‑comparison check to confirm the teaser discount is genuine and not simply a baseline price reduction.
November: Black Friday, Cyber Monday, and Holiday Travel
The November shopping climax offers the deepest, most publicized discounts across virtually every category. While the hype can be overwhelming, focusing on a pre‑written list and using price‑tracking tools can prevent impulse overspending. For travel, many airlines extend "Black Friday" fare drops through early December, providing a window to secure holiday trips at a fraction of peak prices.
Remember to verify coupon code expiration dates—some are only valid for the first few hours of the sale. Apply cashback portals in conjunction with retailer offers for an extra rebate on top of the discount.
December: Year‑End Clearance and Gift‑Ready Deals
December’s final weeks feature clearance events aimed at clearing out remaining holiday inventory. Look for "last‑minute" deals on toys, electronics, and fashion accessories that often include free shipping incentives. This period also sees retailers offering gift‑card bonuses—receive an extra $10‑$20 gift card when you purchase a $100 card, effectively reducing the net cost of future purchases.
Before finalizing a purchase, double‑check return policies, especially for gifts. Extended holiday returns are common, but some items—like personalized goods—may be final sale.
Takeaway: By aligning your purchases with the natural ebb and flow of retail cycles—post‑holiday clearances, seasonal refreshes, and holiday‑driven promotions—you can consistently capture meaningful savings. Use price alerts, reputable coupon sources, and clear comparison criteria to ensure each deal is genuine, and you’ll turn every shopping trip into a strategic win.
MISSION promo code FAQ
Does MISSION have promo codes?
Yes. There are currently 2 active MISSION offers on WaveDeals, with savings up to 25% OFF.
How do I use a MISSION coupon code?
Click “Show Code” on the offer you want above to reveal and copy it, then paste the code into the promo box at MISSION checkout and apply it before paying.
How many MISSION coupons are working right now?
We list 2 MISSION codes and deals that our team checks regularly. Codes that stop working are removed.
What is the best MISSION discount available today?
The top MISSION offer right now saves you 25% OFF. Reveal the code above to use it.
How often are MISSION promo codes updated?
Daily. This page was last refreshed on June 25, 2026, and our automated sync adds new MISSION codes as they go live.
Can I use more than one MISSION coupon code?
Usually only one promo code applies per MISSION order, but you can often combine a code with an ongoing sale or free-shipping offer. Try the highest-value code first.
MISSION reviews
No reviews yet. If you have shopped at MISSION, yours would be the first — it helps the next reader decide.
Write a review
Editor's note
I personally maintain this “MISSION” page. Working at WaveDeals since 2016, I check every shopping promo code against the retailer's terms — which products qualify and which are excluded — and keep the list fresh as offers expire. My advice for MISSION: combine a valid code with an active sale for the biggest discount, and watch for free-shipping thresholds. Bear in mind offer terms can change, and certain codes are limited by delivery region.